
Regulation Without Primary Keys Makes Compliance Automation Just Chat
Why a stable record identity contract, not a better model, is the compliance asset: minimum key requirements, five tests that separate record-level controls from narrative summaries, and a vendor-neutral evaluation checklist.
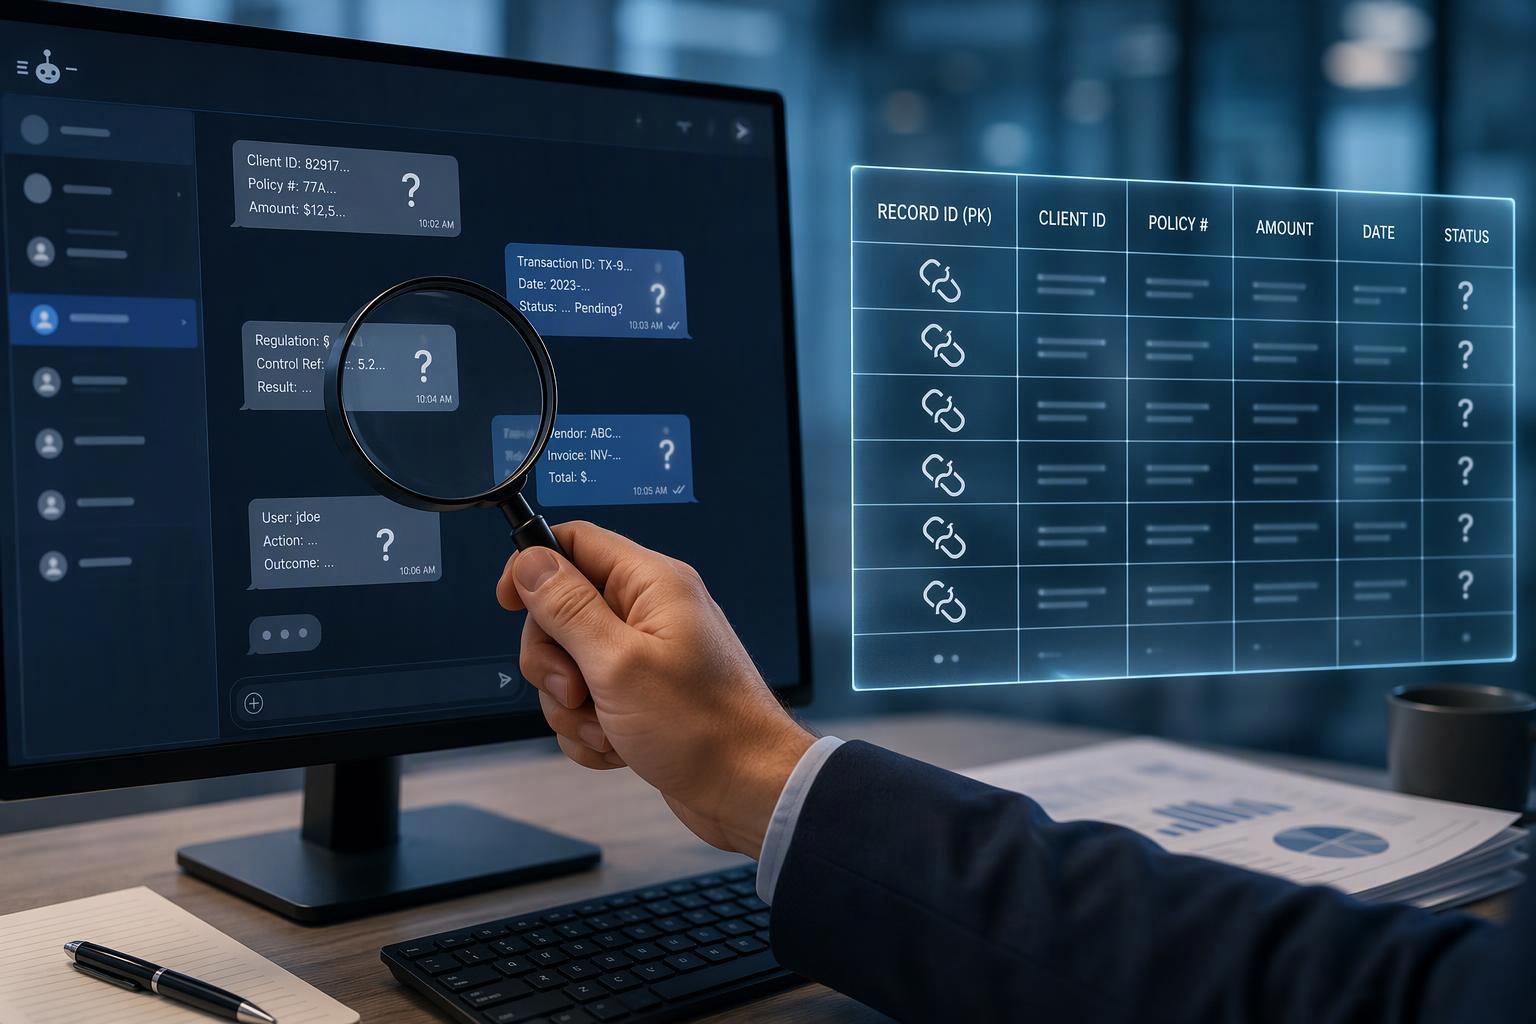
A conversational compliance interface is a retrieval layer. It takes a question, finds candidate material, and generates an answer. That is a useful front door. It is not evidence. When an auditor asks you to reconstruct the state of one specific record at one specific time — who changed it, what it looked like before, and what fed into it — the system has to resolve that request to an identified record and follow its history. If no stable identifier exists, there is nothing to follow, and the fluent answer becomes the only artifact you can produce.
The position here is simple: the identity contract, not the model, is the compliance asset. This article explains why chat appears sufficient, what the minimum identity contract must contain, how to test whether a control executes against identified records or merely summarizes them, which failure modes surface first, and how to evaluate a platform's guarantees without accepting marketing claims.
The demo answers questions; the auditor asks for a record
A conversational interface is good at several things. It can summarize a policy, retrieve a clause, explain a control's intent, and draft a narrative for a control owner. Those are real gains in time and access. None of them is an audit request.
An audit request has a different shape. It names a record, a period, and a question about that record: show every state of this transaction between these dates, identify who changed each field, and demonstrate that the population you drew from was complete. The evidence has to resolve to an identified record, and the trail has to survive the auditor's own inspection.
Regulatory expectations are written in that direction. PCAOB staff reported that approximately 17% of the total comment forms in each of the 2021 and 2022 inspection cycles contained deficiencies where the auditor did not perform sufficient procedures to test, or sufficiently test controls over, the accuracy and completeness of company-produced information or other data and reports (PCAOB staff spotlight, April 2024). The same document sets out the applicable standard: under AS 1105, when company-produced information is used as audit evidence, the auditor should test its accuracy and completeness or test the controls over it, and evaluate whether it is sufficiently precise and detailed. Accuracy and completeness are properties of a defined population, which means someone has to be able to define that population precisely.
Other regimes point at the same requirement from different angles. For electronic records in FDA-regulated contexts, 21 CFR 11.10(c) requires protection of records to enable their accurate and ready retrieval throughout the retention period, and 11.10(e) requires secure, computer-generated, time-stamped audit trails that record the date and time of actions that create, modify, or delete records, with changes that do not obscure previously recorded information. Under the GDPR, Article 5(2) makes the controller responsible for, and able to demonstrate, compliance, and Article 30(4) requires the record of processing activities to be made available to the supervisory authority on request.
Read together, these are not requests for a summary. They are requests for a retrievable, identified, time-stamped record. A chat answer is a derived artifact. It becomes evidence only when it resolves to such a record, and the resolution has to be inspectable by someone other than the system that produced the answer.
Why the conversational layer looks sufficient until it isn't
The illusion is easy to understand once you see where it comes from. A chat interface compresses the retrieval path. The user types a question, the system returns a fluent, specific-sounding answer, and the user infers that the system knows the record. Fluency, however, is a property of generation. It is not a property of identity resolution.
The difference shows up in the join. When the auditor asks for every state of record X between date A and date B, the system must join audit events, versions, and source records on a key that is stable across time and across systems. If that key is an email address, a person's name, or a row number that was reassigned after a deletion, the join does not fail loudly. It returns the wrong rows, or drops the right ones, and the output still looks plausible.
Identity is a control requirement in the standards, not a user-experience nicety. NIST SP 800-53 AU-3 requires audit records to contain information establishing what type of event occurred, when, where, its source and outcome, and the identity of any individuals, subjects, or objects and entities associated with the event. In the healthcare context, 45 CFR 164.312(a)(2)(i) requires unique user identification — a unique name or number for identifying and tracking user identity — and 164.312(b) requires mechanisms that record and examine activity in systems containing electronic protected health information.
These provisions are about attributing events to identified parties. A system that cannot resolve a record to a stable key cannot satisfy them, however well it answers questions. And the failure stays invisible in the demo, because the demo asks the questions the system was tuned to answer, against the records that happened to resolve cleanly.
The minimum identity contract for a compliance record
The identity contract is a design decision your organization makes. No single regulation hands you a field list. The sourced requirements above set a floor: identified actors, time-stamped events, prior states that are not obscured, and records retrievable on request. The contract is how you meet that floor in a way an auditor can inspect.
A workable minimum has five elements.
An immutable surrogate key, assigned at creation and never reused. This is the anchor. It is independent of business attributes, so a change of name, email, or account number does not break the chain. NIST AU-3's requirement to identify the objects and entities associated with an event depends on objects having an identity that persists.
The source-system identifier plus the source system's own key. The surrogate key tells you the record exists in your platform. The source pointer tells you where it came from and lets you reconcile back to the system of record. Without it, lineage stops at the ingestion boundary.
Effective-from and effective-to dates, distinct from system timestamps. Business validity and system time are different questions. An auditor asking what the record said on a given date needs the business-effective interval; an engineer debugging a pipeline needs the ingestion timestamp. Conflating them produces answers that are precise and wrong.
A version or sequence number. 21 CFR 11.10(e) requires that record changes not obscure previously recorded information. Versioning is the mechanism that makes that possible: each state is retained, ordered, and attributable.
Lineage pointers to the inputs and transformations that produced the record. This is what lets you answer where a value came from and which upstream change produced a downstream difference. It is also what makes a completeness argument possible, because you can show the population and its provenance.
GDPR Article 30 is a useful reminder that the record itself is a deliverable: a written description of processing categories, recipients, transfers, retention limits, and security measures, available to the supervisory authority on request. That is a record about processing, not a primary key. But producing it reliably, and keeping it current as processing changes, depends on the same discipline of identified, versioned, traceable entries.
Treat the contract as the floor plus your own risk assessment. The regulations tell you what must be demonstrable. They do not tell you which fields your records need in order to demonstrate it.
Testing whether a control executes against records or summarizes them
The test is a sequence, and each step has a checkpoint. Run it against a non-production copy of a compliance-relevant dataset, and record what the system returns, not what it says about itself.
Step 1: The state transition test. Pick one record. Change a field. Ask the system to produce the pre-change state, the post-change state, the actor, and the timestamp for each. Checkpoint: a system that executes against identified records returns both states and the transition between them, each tied to the same key. A system that summarizes returns a narrative that may be accurate in substance but has no resolvable record behind it. If you cannot take the identifier from the answer and query the record directly, the test has failed.
Step 2: The reused-key test. Take a record whose key was reused after a deletion, or construct one in the test environment. Ask for its full history. Checkpoint: the system should distinguish the two lives of that key, or refuse and explain. If it merges them into a single continuous history, the key is not immutable and the contract is broken.
Step 3: The merge test. Take a record assembled from two source systems. Ask for its lineage. Checkpoint: both sources should appear, with the transformation that combined them. A single lineage that shows only the surviving source is a silent merge, and the audit trail now asserts a history that never existed.
Step 4: The zero-row test. Ask a question whose correct answer is no records. Checkpoint: the system should return nothing and say so. A system that produces a plausible record or a hedged narrative where the answer is empty is generating, not retrieving, and you cannot tell which mode it is in from the output alone.
Step 5: The entitlement test. Ask for a record the requesting user is not entitled to see. Checkpoint: the system should refuse, and the refusal should be logged. A leak here is both a compliance failure and evidence that the conversational layer is not respecting the same permission boundaries as the underlying data.
These are acceptance criteria, not a product review. They test whether the identity contract from the previous section is actually in force. If the contract is absent, the tests will fail regardless of which model or interface sits on top, and passing them requires the contract to be in place first.
The failure modes that surface first
The following failure sequence is an illustrative inference from how identity systems behave, not a set of observed incidents. It describes what tends to surface first when keys are mutable or non-unique.
Email as key. Email addresses change when people marry, move between organizations, or switch providers. They are reassigned within organizations, and they are not unique across systems. A join on email silently merges two people who shared an address at different times, or splits one person whose address changed. The observable symptom is a duplicate actor in the trail, or a gap where a person's history should continue. The control is an immutable surrogate key with email stored as an attribute, not as the identifier.
Recycled identifiers. A row number or sequence reused after deletion makes two distinct records indistinguishable. The World Bank's ID4D guidance describes this pattern in identity systems generally: some systems have less reliable identity records because of a lack of deduplication, non-unique identifier generation such as recycling ID numbers over time, or weak identity proofing (World Bank ID4D). The symptom is a transition with no prior state, or a history that appears to jump. The control is a key that is never reused, plus a tombstone rather than a hard delete, so the record's end is itself an event.
Silent merges. When two source records are merged, the surviving key absorbs the other's history. The audit trail then shows a single lineage that never existed, and the merged-away record becomes unreachable. The symptom is a lineage that shows one source where two were expected. The control is to record the merge as its own event, with its own lineage node, so the merge is visible and reversible in the record's history.
The common thread is that each failure produces a plausible output. None of them throws an error the demo would surface. That is why the tests in the previous section matter more than the demo: they are designed to make the failure visible before an auditor does.
Evaluating a platform's identity and lineage guarantees
The framework below is vendor-neutral. Apply it to any platform, including Singdata, and treat vendor performance figures as claims to validate in your own environment rather than as established facts.
Criterion 1: Immutable key independent of business attributes. Test: create a record, change its business attributes, and confirm the key is unchanged and the history is continuous. Then confirm the key is never reused after deletion.
Criterion 2: Prior versions retained, not overwritten. Test: modify a record several times and retrieve each prior state with its timestamp and actor. Confirm that no state has been obscured.
Criterion 3: Record-level lineage, not just table-level. Test: trace one record back through its transformations to its sources. Table-level lineage will tell you which jobs touched which tables; it will not tell you which inputs produced this row.
Criterion 4: Point-in-time reconstruction without a full rebuild. Test: ask what the record looked like at a specific past time and measure whether the answer comes from retained history or from a recomputation. Recomputation is acceptable only if it is deterministic and produces the same result the record had at that time.
Criterion 5: API access to the key and lineage. Test: have someone other than the platform's own interface query the key and lineage directly. If the auditor cannot reach the evidence without going through the chat layer, the evidence is not independently inspectable.
Criterion 6: Merge distinguished from update. Test: merge two records and confirm the system records a merge event with both sources, rather than presenting the result as an ordinary update.
Singdata's lakehouse stores data in open formats in the customer's own object storage, which is one architecture in which an identity contract can be enforced at the storage layer rather than only in an application. That is a structural observation, not a guarantee. Whether the contract is actually enforced is what the six tests above are for, and the answer should come from your environment, not from a product page.
The strongest objection: the model will get better
The strongest objection is that models and retrieval will keep improving, so the identity contract is a temporary concern. Better retrieval will find the right record more often, and better generation will produce more reliable narratives. Why build a deterministic contract for a problem that is shrinking?
The answer is that better retrieval improves the probability of finding the right record. It does not create a stable identifier where none exists, and it does not make a mutable key immutable. If the underlying data has no stable key, a more capable model has more ways to produce a confident answer that cannot be traced. The failure becomes less frequent and harder to detect, which is worse for audit, not better.
A probabilistic system that is right 95% of the time is worse for audit than a deterministic join that is right whenever the key is sound, because the auditor needs to know which case they are in. A deterministic join tells you: this is the record, this is its history, this is the population. A probabilistic answer tells you: this is probably the record, and you have no way to tell whether this is one of the 5%.
There is a real role for models here. Entity resolution can help reconcile records across systems. Lineage inference can help reconstruct provenance where documentation is thin. Those are construction tasks, and they are valuable. But the contract itself must be deterministic and inspectable. AI can help construct the keys. It cannot substitute for them.
What to do before the next demo
Before the next demo, run this checklist against the platform in question. Each item is a question with a verifiable answer, not a reassurance.
Confirm an immutable key exists for every compliance-relevant record, assigned at creation and never reused.
Confirm prior versions are retained and retrievable, with actor and timestamp for each state.
Confirm lineage is recorded at the record level, not only at the table level.
Run the five tests from the testing section: state transition, reused key, merge, zero rows, and entitlement.
Confirm the auditor can query the key and lineage directly, without going through the conversational interface.
The conversational interface is the right front door. It makes compliance data accessible to people who would otherwise wait on a ticket. But the identity contract is the load-bearing structure, and a compliance automation program that skips it is a chat program with a compliance label.
The practical next step is to pick one compliance-relevant dataset and run the state transition test. If the system cannot return both states with the same key, actor, and timestamp, you have found the gap before an auditor did.
FAQ
Does a data warehouse alone satisfy the contract? No. A warehouse provides storage, query, and often versioning features, but it does not impose the key discipline. Whether the contract holds depends on how records are keyed, versioned, and linked to lineage, which is a design decision above the storage layer.
Does GDPR's record-of-processing requirement mandate a primary key? Article 30 requires a written record of processing activities, available to the supervisory authority on request. It does not name a primary key. In practice, producing and maintaining that record reliably as processing changes depends on identified, versioned entries, which is what the contract provides.
Can the tests be run without engineering support? Partially. The entitlement and zero-row tests can be run by a compliance or risk owner through the interface. The state transition, reused-key, and merge tests need query access to the underlying records, so they require engineering involvement.
Can an AI agent be trusted to enforce the contract? An agent can operate within the contract — retrieving identified records, assembling histories, and flagging gaps. It cannot replace the contract, because enforcement requires deterministic keys and inspectable lineage that exist independently of any model's output.
find out more
https://singdata.com/trending/iot-sensors-vs-camera-analytics-kpi/
https://singdata.com/trending/author/aaamkvm24qs2ekeu/?page=17
https://singdata.com/trending/mirror-sync-vs-merge-on-read-choosing-the-best-sync-method/